There seems to be no end to Black October in the world of cybersecurity. After finding severe flaws in PHP and eMudhra, there is now another critical vulnerability which may put millions of...
AI found PHP’s decade-old flaws in two days. But patching at that speed means letting AI act on its own, and nobody’s guarding what it can touch.
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) on Monday confirmed active exploitation of the recently patched PHP2Shell flaws by adding them to its Known Exploited...
CISA added the widely publicized PHP vulnerabilities to the KEV, but didn't specify what kind of exploitation it was observing.
The U.S. government cyber agency warns that hackers have figured out a way to exploit the popular PHP software, used in 70% of the web's software.
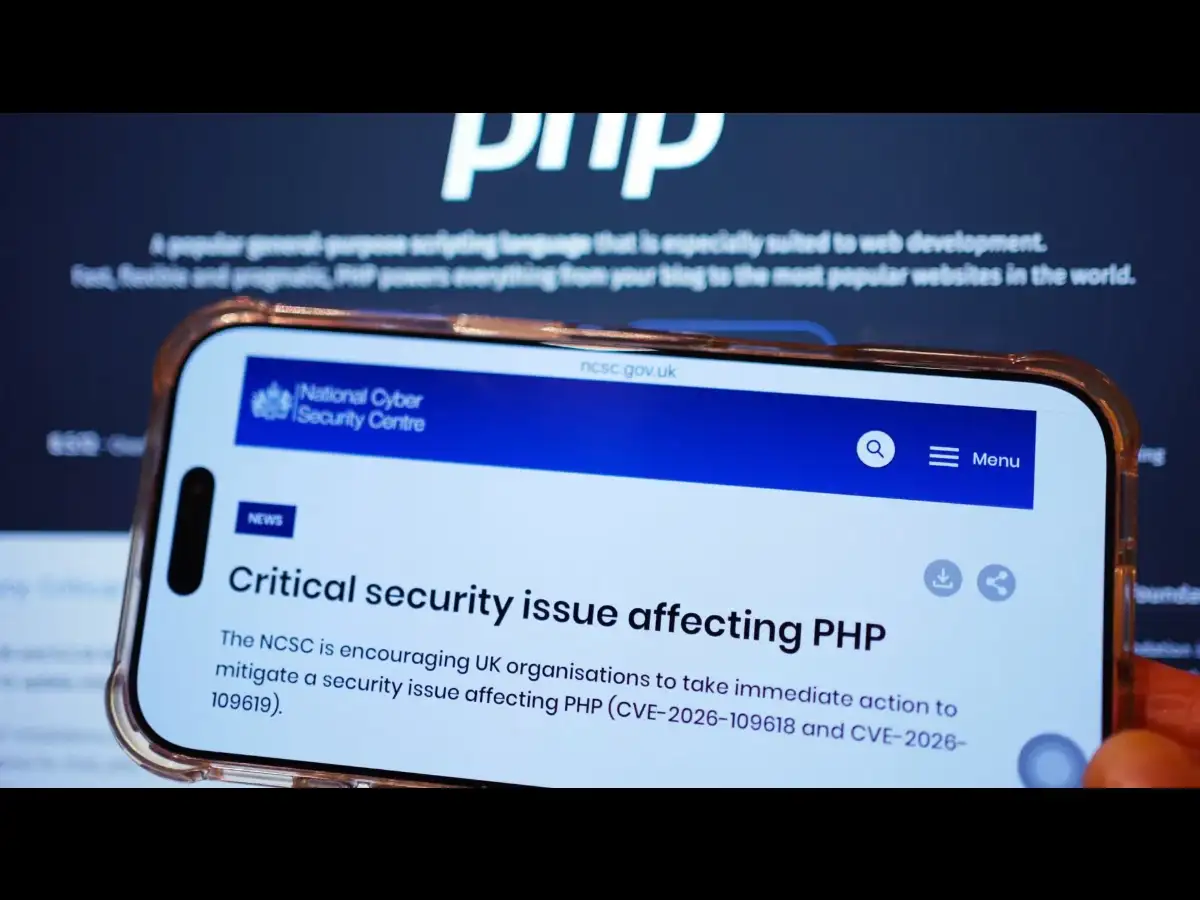
Last week, two critical cybersecurity flaws in the PHP programming language were discovered with the help of AI. Subsequently, Cert-In issued advised organisations to apply security patches....
Multiple tech companies and projects have recently pushed patches for a vulnerability called "HTTP2Shell" which could enable remote code execution (RCE) attacks, similar to the recent "PHP2Shell"...
Dream has reported a PHP2Shell attack chain that it says compromised 25 servers, including systems in a U.S. government-affiliated environment. Its October 26 investigation describes an exposed...
After live exploitation of PHP2Shell was verified at the weekend, the US' Cisa cyber agency updates its vulnerability catalogue, urging organisations to prioritise their fixes.
A major vulnerability in the PHP programming language has emerged, impacting numerous global websites. In response, governments and cybersecurity firms are strongly recommending urgent updates to...
"By far the highest quality confirmation of in-the-wild php2shell exploitation I've seen"
First reported:
First saved on ClustZ:
Coverage updated:
We use cookies to improve your experience and analyze site traffic. By clicking "Accept", you agree to our use of cookies. See our Privacy Policy.