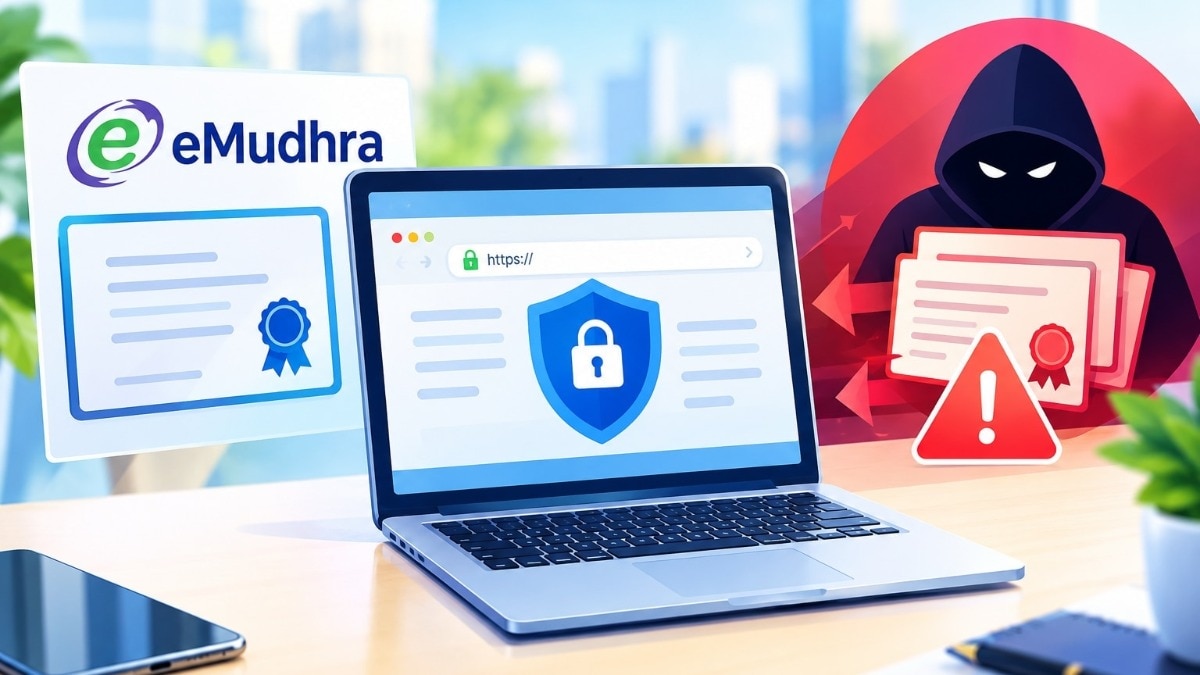
The issue came to light after researchers identified weak cryptographic keys in eight intermediate digital certificates linked to eMudhra.
Shares of the company fell 20% and hit the lower circuit after the security flaw was highlighted. The discovery has raised concerns that attackers could use the certificates to create fake...
CERT-In says the flaw could also allow malicious software to be passed off as coming from a trusted publisher.
eMudhra Ltd confirmed that its Indian digital signature services remain secure despite a security flaw affecting its global TLS certificate business.
eMudhra—has now come under the scanner for putting out weak certificates that, if exploited, could bring serious harm to netizens given that eMudhra happens to be one the largest companies of its...
Its Indian digital signature and eSign services remain unaffected, while the incident could carry reputational risks, executive vice president Kaushik Srinivasan said.
India’s cybersecurity agency CERT-In has issued an advisory warning about a security compromise involving eight intermediate digital certificate authorities linked to Indian company eMudhra. The...
eMudhra (@eMudhra) October 20, 2026The company stressed that the problem was limited to these certificates and did not affect its root certificate authority's private keys or other intermediate...
The ministry said the reported security incident pertains to eMudhra’s global certificate business, and its impact on Indian websites is very limited.It also said some social media accounts were...
eMudhra’s digital certificates were found to have weak security keys, risking data interception and manipulation. Major tech companies block affected certificates as eMudhra investigates and works...
Google, Apple and Mozilla have blocked eight digital certificates issued by the Indian certificate authority eMudhra after researchers found dangerously weak private keys. The flaw could let...
Private keys were recoverable almost instantly, potentially enabling attackers to impersonate trusted websites.
eMudhra is an Indian digital trust and cybersecurity company that provides digital signatures, electronic authentication and website security services
Google and Mozilla have blocked intermediate certificates issued by Bengaluru-based eMudhra after a researcher showed their private keys could be recovered because they were generated with little...
Eight eMudhra CA keys were compromised. Chrome, Firefox, Apple and Microsoft blocked them. Here is what happened, the risks and how to secure systems.
Think of a digital certificate as a website's official ID card. It is what powers the little padlock icon in your web browser, promising that your connection is safe and your data is secure. But...
eMudhra says that it has revoked eight certification authorities in its Global TLS business.
The private keys of eight eMudhra intermediate certificate authority (CA) certificates are compromised, Mozilla and Google's Chrome Root Program confirms on October 20. An intermediate CA signs...
Massive clean-up job under way because this mess makes it possible to impersonate any website or service
Eight eMudhra intermediate certificates had weak private keys that could enable website impersonation, prompting Google, Mozilla and Cloudflare to act to protect internet users
Eight private keys from eMudhra Ltd., used for web security certificates, have been leaked, affecting government websites and major internet browsers globally.
eMudhra exposed eight weak private keys, prompting browser vendors to block affected certificates. Here is what happened and what remains unresolved.
Many government websites, including the Aadhaar issuer UIDAI and the income tax filing portal, use digital certificates or other technology from the Bengaluru-headquartered firm; no indication...
First reported:
First saved on ClustZ:
Coverage updated:
We use cookies to improve your experience and analyze site traffic. By clicking "Accept", you agree to our use of cookies. See our Privacy Policy.