Cheap Android TV boxes sold to consumers may have shipped with a pre-installed backdoor that enrolled more than 1.3 million devices into the XCPE botnet, according to a Google Threat Intelligence...
Google discovered and shut down a backdoor built into millions of Google TV and Android TV set-top boxes built by Videostrong Technology Co.
The malware reinstalls itself from protected firmware after you delete it, and researchers have linked it to 206 TV box models.
The backdoor was discovered in the firmware of multiple Videostrong devices, such as the Mecool KTI, as well as several white-label Android TV boxes. Seattle-based cybersecurity and fraud...
A Chinese company allegedly intentionally infected its devices with malware and later sold access to a botnet to criminals.
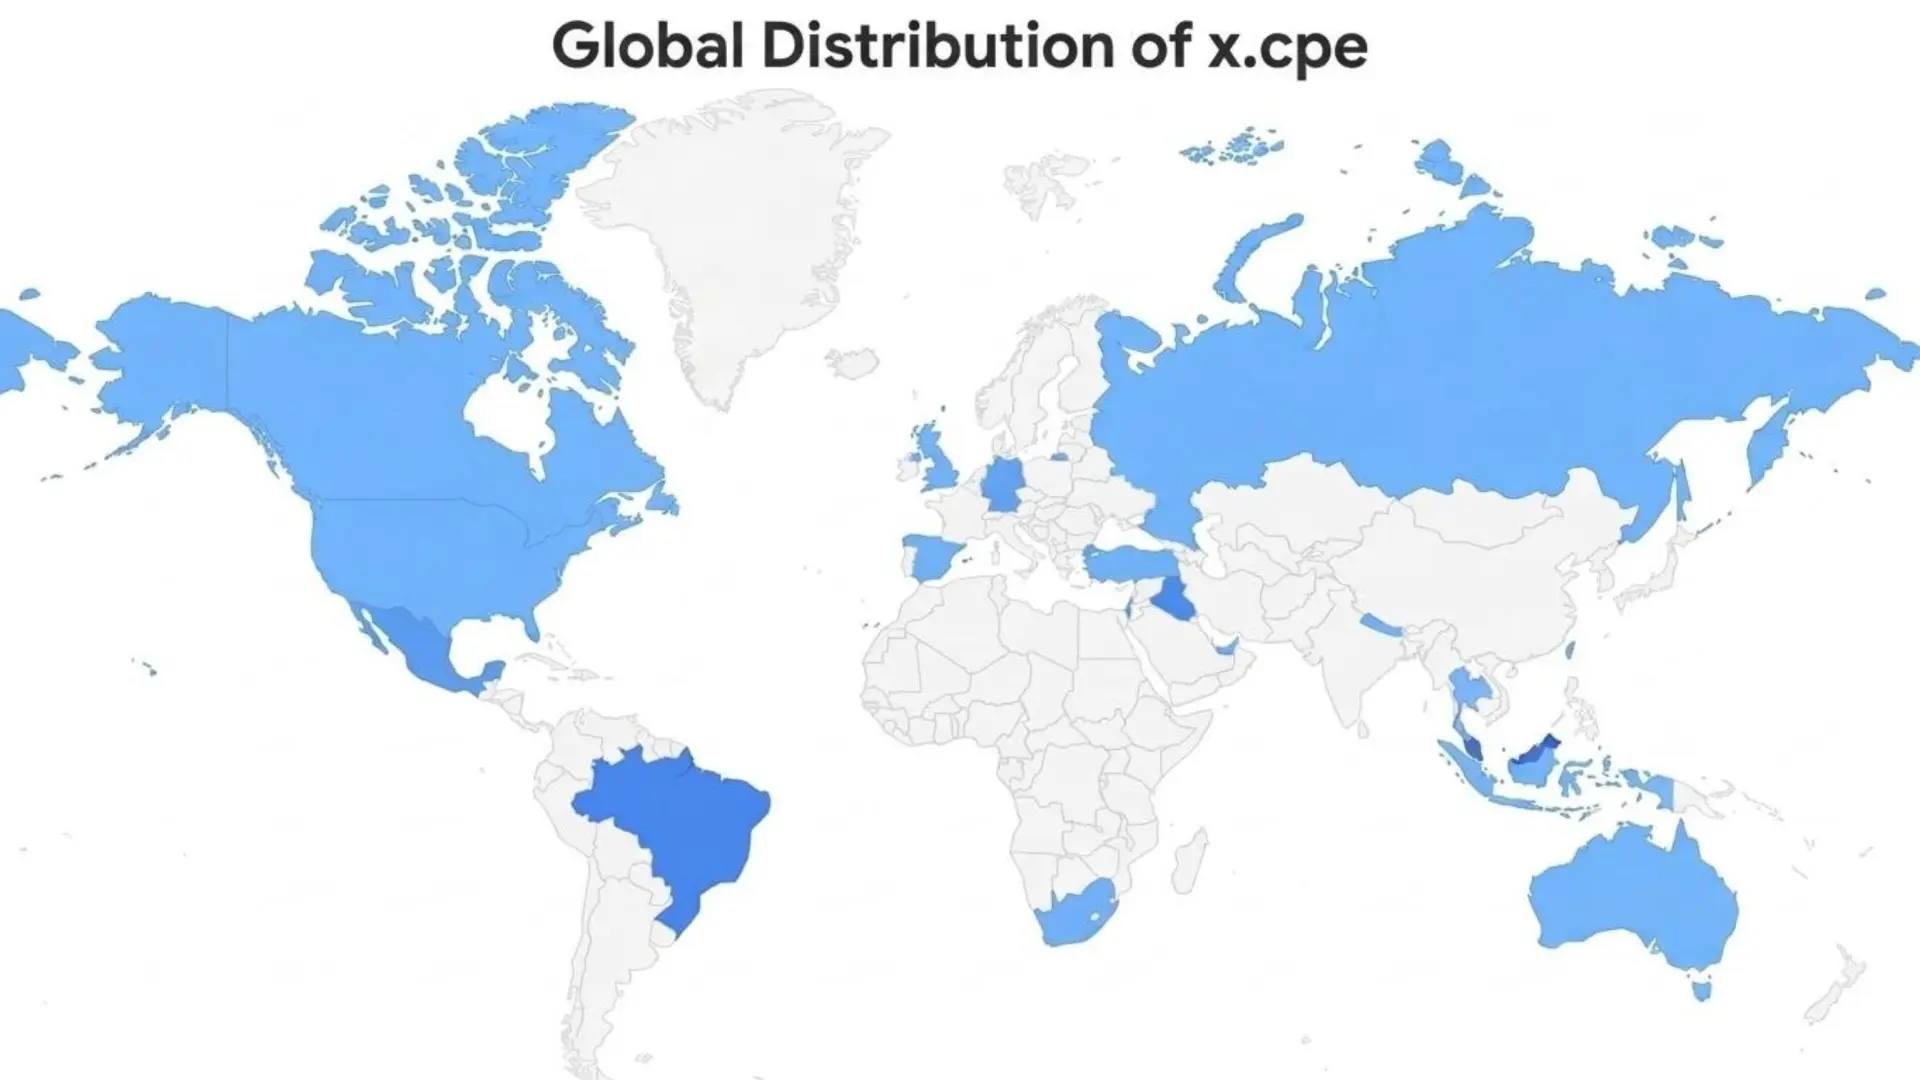
Google has disrupted the global XCPE botnet, an illegal operation that controlled over 1.3 million Android TV set-top boxes worldwide.
In a significant security breach, Google has cut ties with Videostrong Co after discovering a malicious backdoor integrated into over 1.3 million devices. This vulnerability enabled hackers to...
First reported:
First saved on ClustZ:
Coverage updated:
We use cookies to improve your experience and analyze site traffic. By clicking "Accept", you agree to our use of cookies. See our Privacy Policy.