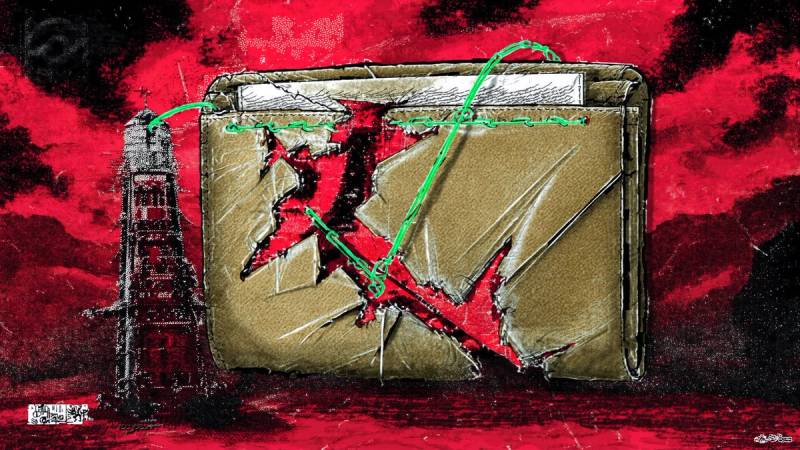
Electrum, one of Bitcoin’s oldest software wallets, published a security advisory on Saturday describing a weakness that attackers were already abusing. TL;DR A bug in the Electrum bitcoin wallet...
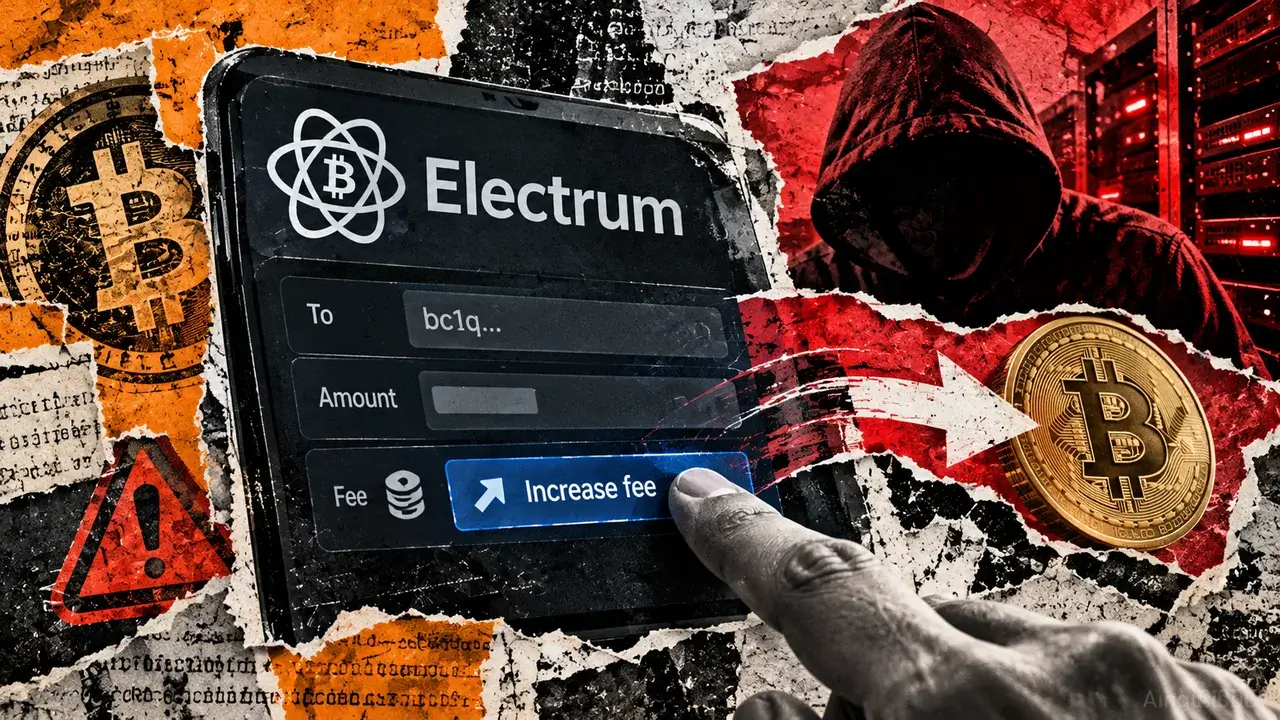
Attackers replaced legitimate transactions with fake ones, then waited for users to approve higher fees. At least one person lost bitcoin before developers patched the flaw.
Version 4.8.3 fixes a malicious-server attack that can turn a manual fee increase into approval of an attacker-directed payment. Read the full story on CryptoSlateUnderstand the crypto stories...
A malicious server can substitute a fake payment, then trick the user into signing it while raising the transaction fee. Developers say one user reported losing money.... Read the full story at...
First reported:
First saved on ClustZ:
Coverage updated:
We use cookies to improve your experience and analyze site traffic. By clicking "Accept", you agree to our use of cookies. See our Privacy Policy.